 Vanta
 Drata
 Secureframe
 Sprinto
 Scytale
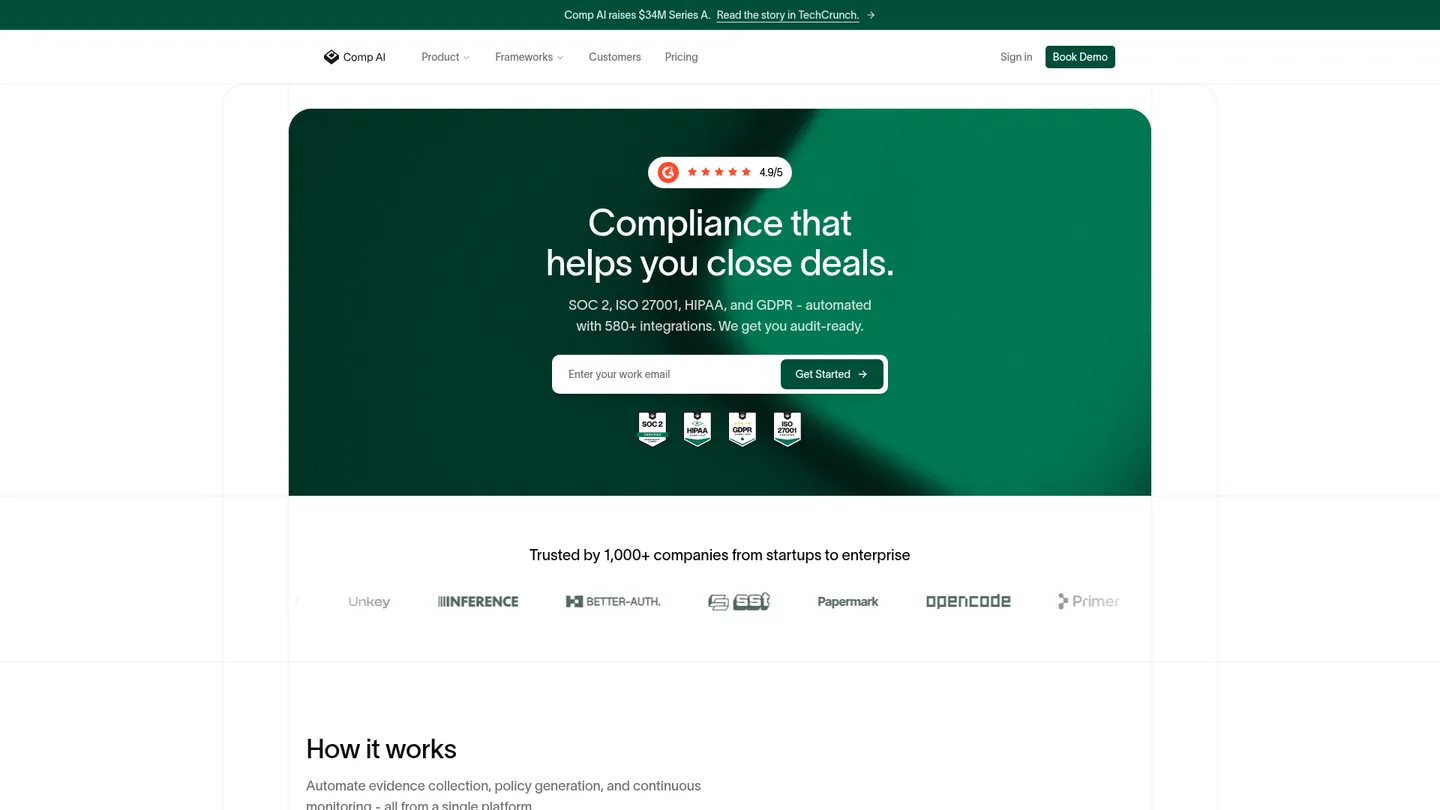
What is Comp AI?
Founded in 2025 and headquartered in Miami, Comp AI combines automated evidence collection, policy workflows and security monitoring. Its commercial open-core platform serves 1,000+ companies and offers hosted and self-hosted deployment.
Comp AI is an AI-native compliance platform that connects to a company’s technology stack and automates evidence collection, policy generation, control implementation and monitoring. Teams can use the hosted product or deploy the open-source core themselves. The workflow covers compliance preparation, vendor assessments, risk management and trust-center publishing, with agents and scheduled checks intended to reduce recurring manual work across security and compliance programs.
The platform supports SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, SOC 1, NIST, ISO 42001, ISO 9001, CCPA, NEN 7510, FedRAMP and other scopes. Features include continuous monitoring, security questionnaires, device compliance, browser automations, AI-assisted penetration tests, vendor-risk workflows and trust-center tools. Its breadth is substantial, while self-hosting requires infrastructure and operational ownership and hosted pricing varies by scope.
Comp AI is aimed at startups and growing companies that need audit readiness, customer-facing security documentation or ongoing compliance operations without assembling a large internal program. Hosted pricing is custom and determined by frameworks, headcount, timeline, audit or penetration-testing needs and trust-center requirements during a 20-minute pricing call. The public repository offers an AGPLv3 open-source core, while the Enterprise Edition is commercially licensed.
Key features
Evidence collection
Automates evidence gathering from connected systems and runs checks after connection and through scheduled jobs.
Policy generation
Uses AI to generate tailored security and compliance policies for the selected program.
Continuous monitoring
Monitors controls and security posture between audit cycles.
Framework mapping
Maps controls across frameworks including SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS and NIST.
Trust center
Provides a live trust center for sharing security and compliance information with customers.
Vendor risk management
Supports vendor assessments, risk profiles and third-party security workflows.
Penetration testing
Offers AI-assisted penetration tests with Markdown or PDF reports, finding triage and an auditable dispute trail.
Comp AI pricing
Current hosted pricing is quote-only and depends on frameworks, company size, timeline and whether audit, penetration testing or trust-center work is included. The official pricing page does not publish a universal paid starting price. The self-hosted core is available under AGPLv3, with infrastructure and operations managed by the customer.
| Plan | Price | What's included |
|---|---|---|
| Self-hosted core | Free software licenseInfrastructure and operating services are customer-managed. | AGPLv3 open-source core, local deployment, customer-managed infrastructure and maintenance |
| Hosted custom plan | CustomScope is set during the pricing call. | Hosted platform, automated evidence collection, policy management, framework workflows, monitoring, support and optional audit, penetration-testing or trust-center services |
Free trial: Demo available; no public trial offer.
Pros & cons
Pros
- Combines evidence, policies, monitoring, vendor risk and trust-center workflows.
- Maps controls across multiple frameworks to reduce duplicate compliance work.
- The open-source core supports customer-controlled deployment.
- Supports recurring evidence collection across a modern software stack.
Cons
- Hosted pricing is quote-only, making budget comparison difficult before a sales call.
- Self-hosting requires infrastructure and ongoing security operations.
- The Enterprise Edition is commercially licensed despite the AGPLv3 open-source core.
- Automation quality depends on connected systems, configuration and human review.
Who is Comp AI best for?
- Startups preparing for SOC 2 or ISO 27001
- Growing teams needing automated evidence collection
- Companies that need a customer-facing trust center
- Engineering-led teams evaluating open-core deployment
Frameworks and use cases
Integrations
Notable customers
Frequently asked questions
How much does Comp AI cost?
+
Comp AI uses custom hosted pricing rather than a public rate card. The quote depends on frameworks, headcount, timeline and whether audits, penetration testing or trust-center work is included.
How long does Comp AI take to set up?
+
The pricing page says most teams connect their stack and begin collecting evidence the same week. Setup timelines depend on scope, integrations and company readiness.
How does Comp AI compare with Vanta?
+
Both products support automated evidence collection and common compliance frameworks. In a comparison evaluation, Comp AI stands out for its AGPLv3 open-source core, optional self-hosting and AI-assisted workflows; pricing requires direct scoping.
Which integrations does Comp AI support?
+
The company claims more than 580 integrations. Named documentation examples include AWS Security Hub, Microsoft Defender for Cloud, Google Cloud Security Command Center, Google Workspace, Rippling, GitHub, Vercel and Linear.
Who is Comp AI for?
+
Comp AI is designed for startups and growing companies pursuing audit readiness or ongoing compliance across security, privacy and regulated frameworks. Its hosted and self-hosted options also suit engineering-led teams with deployment preferences.
Is Comp AI secure and accurate?
+
The trust center lists SOC 2 Type 1, SOC 2 Type 2, ISO 27001, GDPR and HIPAA as compliant, with 26 policies and 44 controls. AI-generated policies, evidence checks and penetration-test results require review against the organization’s actual scope.
Sources
Facts and pricing verified on October 19, 2026. Vendors change pricing often, so confirm with Comp AI before buying. How we research