 Vanta
 Drata
 Secureframe
 Sprinto
 Thoropass
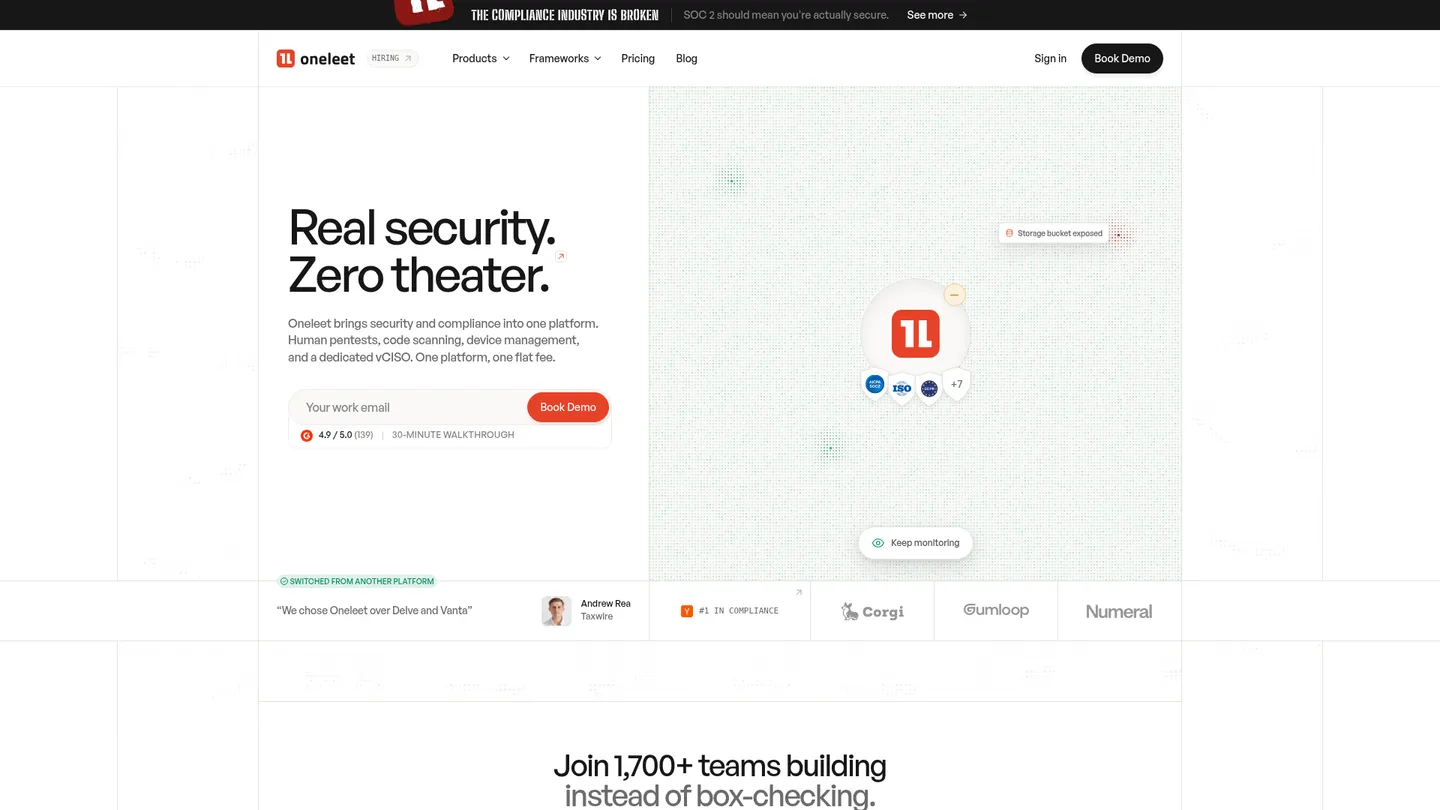
What is Oneleet?
Founded in 2022 and headquartered in Amsterdam, Oneleet combines compliance automation with penetration testing, security monitoring and vCISO support. The company says it serves 1,000+ teams and raised a $33 million Series A in 2025.
Oneleet is a security and compliance platform that connects a company’s cloud, code and workforce tools, then maps the resulting controls and evidence to a chosen framework. Its guided compliance journey turns gaps into tasks, while automated monitors continue checking controls after the audit. Oneleet adds a dedicated vCISO, expert review and managed audit support, aiming to make compliance work part of an operating security program rather than a one-time evidence-collection project.
Coverage spans program and control management, access reviews, risk and vendor management, employee security, device management, security training, trust centers, questionnaires, code and dependency scanning, cloud security, attack-surface monitoring and penetration testing. The breadth is a meaningful differentiator, but it also means buyers are adopting managed security services as well as software; independent auditors still issue the formal report or certification, and third-party costs may apply. Integrations require meaningful read permissions, with some optional write access for GitHub autofixes.
Oneleet is aimed at startups, scale-ups and larger organizations that need customer-facing assurance and want to consolidate compliance, testing and security operations. Its materials describe startup, mid-market and enterprise use, with support for custom controls and multiple frameworks. Pricing is quote-based rather than self-serve: the company asks buyers to book a demo, and the quote can cover the platform, pentest and audit support while third-party fees are quoted before signing. There is no published free plan or trial.
Key features
Framework mapping
Maps one control set across SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, NIST and other frameworks.
Continuous monitoring
Runs automated monitors across connected systems to identify control gaps and drift in real time.
Security testing
Combines code and dependency scanning, cloud checks, attack-surface monitoring and OSCE-certified penetration testing.
Audit management
Provides expert review, audit coordination and support for independent third-party audits.
Risk and vendors
Maintains a risk register and workflows for discovering, assessing and tracking third-party vendors.
People and devices
Uses an employee portal, security training and an agent to monitor device encryption, screen locks and antivirus.
Trust and questionnaires
Publishes a Trust Center and uses existing policies and evidence to help answer customer security questionnaires.
Oneleet pricing
Oneleet does not publish a starting price or standard tier prices. Its pricing page says quotes depend on the buyer’s needs, while the homepage describes a bundled platform, penetration testing and audit support; third-party fees are quoted before signing. The package can therefore be broader than software-only compliance tools, but buyers should request an itemized quote for recurring software, services, audits and any framework-specific work.
| Plan | Price | What's included |
|---|---|---|
| Startup | Custom | Compliance automation, security monitoring, expert guidance, scope defined in the proposal |
Free trial: A demo is available; buyers are directed to book a demo for a custom quote.
Pros & cons
Pros
- Combines compliance workflows with penetration testing, code scanning, cloud security and attack-surface monitoring.
- Maps controls across multiple frameworks so completed work can support later certifications.
- Includes human review and vCISO guidance instead of relying only on automated evidence collection.
- Supports custom controls, Trust Center publishing and questionnaire workflows for customer assurance.
Cons
- Pricing is custom and there is no public entry price, free plan or standard trial.
- The bundled security-services model may be more than a buyer seeking lightweight compliance software needs.
- Formal reports and certifications still come from independent auditors, so the platform cannot replace the external assurance provider.
- Some integrations require broad read permissions, while optional GitHub autofixes require repository write access.
Who is Oneleet best for?
- Startups that need SOC 2 readiness and real security testing in one engagement.
- Scale-ups selling to enterprise buyers across more than one compliance framework.
- Teams that want a vCISO and managed audit coordination rather than software alone.
- Security-conscious organizations consolidating compliance, pentesting, device and cloud tools.
Frameworks and use cases
Integrations
Frequently asked questions
How much does Oneleet cost?
+
Oneleet publishes custom pricing rather than a starting amount or standard public tiers. The company says buyers should book a demo, and quotes can include the platform, penetration testing and audit support; third-party fees are quoted before signing.
How does Oneleet help a company become audit-ready?
+
A buyer connects cloud, code and workforce tools, selects a framework and follows a guided task path. Automated monitors collect evidence and flag gaps, while Oneleet experts review work and help coordinate the independent audit. The audit window itself still depends on the selected report or certification.
How does Oneleet compare with Vanta?
+
Vanta is primarily known for compliance automation, while Oneleet positions itself as a broader security-and-compliance service that includes a human penetration test, code scanning, device management and vCISO support. Buyers should compare the quoted bundle, included auditor services, framework scope and integrations rather than assuming either platform is cheaper.
Which integrations does Oneleet support?
+
Documented integrations include Slack, AWS, Google Workspace and GitHub. The connectors monitor items such as users, access, cloud resources, repositories and vulnerabilities; permissions vary, and GitHub code autofixes can require write access.
Who is Oneleet designed for?
+
Oneleet targets startups, mid-market companies and enterprises that need SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS or related assurance. It is especially suited to organizations that want compliance software plus security testing and an ongoing vCISO, rather than a narrow evidence tracker.
Does Oneleet guarantee compliance or replace an auditor?
+
No. Oneleet provides controls, evidence automation, monitoring, testing and audit support, but an independent auditor issues the SOC 2 report or certification body handles ISO 27001 certification. The outcome still depends on the customer’s scope, remediation and audit engagement.
Sources
Facts and pricing verified on October 19, 2026. Vendors change pricing often, so confirm with Oneleet before buying. How we research