 Vanta
 Drata
 Secureframe
 Hyperproof
 Optro
What is RegScale?
RegScale is headquartered in McLean, Virginia, with R&D in Knoxville, and reported a 70-plus-person team in 2025. It serves dozens of large-enterprise customers with continuous controls monitoring and compliance-as-code.
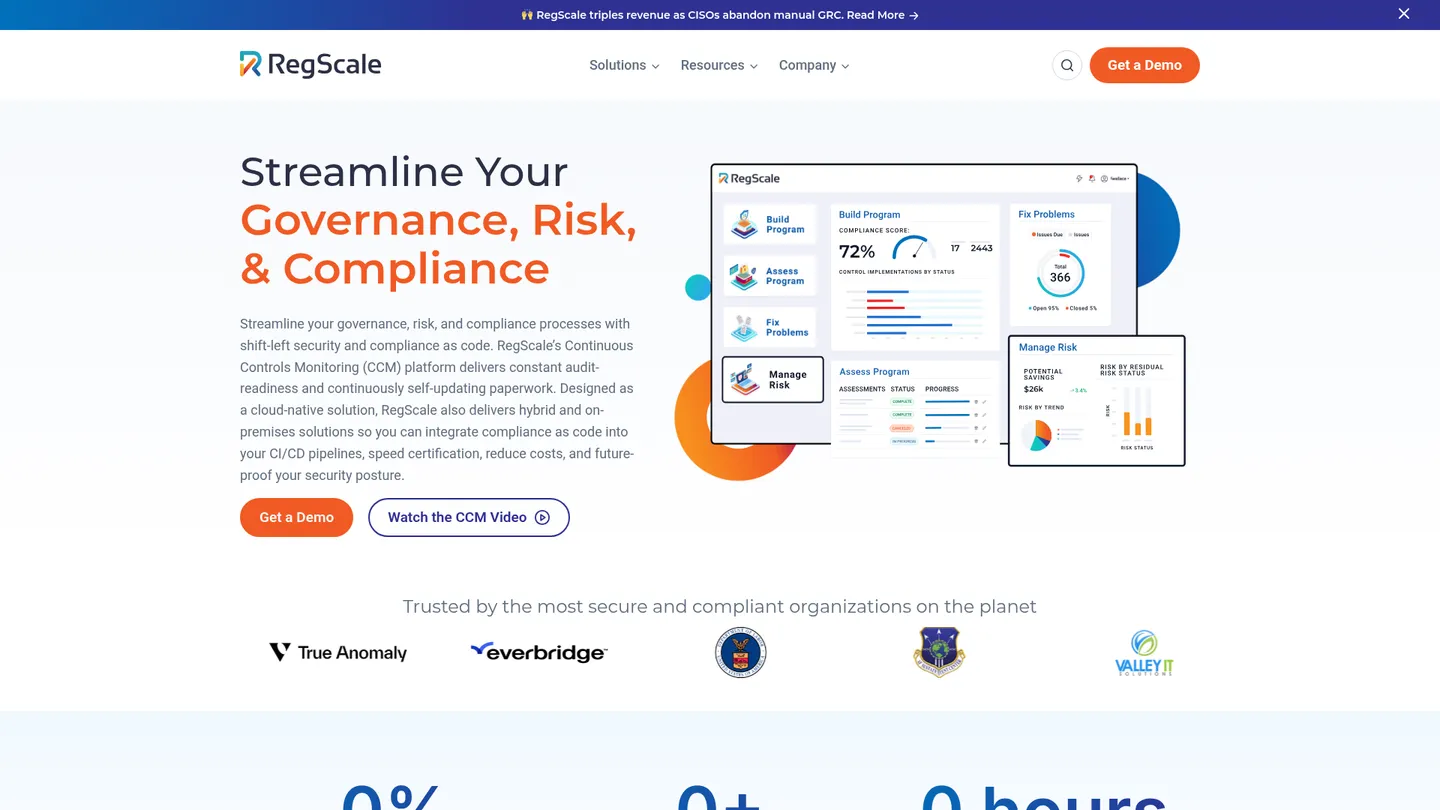
RegScale is a continuous controls monitoring platform that connects security and cloud telemetry, vulnerability scanners, ITIL systems, and CI/CD pipelines to compliance frameworks. Its compliance-as-code model uses machine-readable controls, automated evidence collection, cross-framework mapping, workflows, dashboards, and AI-assisted analysis to keep security plans and audit artifacts current. Organizations can operate it as a cloud service or deploy it on premises and in air-gapped environments, supporting federal and commercial programs.
The platform covers policy and compliance management, risk registers, third-party and enterprise risk, audits, issues and POA&M remediation, evidence management, reporting, control testing, authorization packages, and DevSecOps workflows. RegScale lists more than 60 natively supported frameworks and more than 75 connectors. The product is designed for complex, multi-framework programs, while G2 reviews identify challenges with reporting, filtering, and customization. These needs should be scoped during implementation.
RegScale is aimed at government agencies, defense contractors, financial-services organizations, technology companies, and other regulated enterprises rather than lightweight self-serve compliance teams. Public pricing is not offered on the vendor site, and the vendor does not publish a free trial. A Community Edition is described as free, while reseller listings show annual enterprise subscriptions from $133,900 for ATO Automation Base SaaS.
Key features
Continuous controls monitoring
Continuously assesses controls and connects live operational evidence to compliance requirements instead of relying solely on point-in-time audits.
Compliance as code
Uses machine-readable controls and standards such as OSCAL, with APIs, webhooks, and CI/CD integration for automated workflows.
Evidence automation
Collects evidence from cloud, scanner, DevOps, ITIL, and security tools and stores it in an evidence locker with hashing.
Framework mapping
Maps shared controls across more than 60 frameworks so teams can assess once and reuse work across programs.
Risk and remediation
Supports enterprise, system, third-party, and audit risk with issues, POA&M tracking, workflows, and remediation reporting.
Authorization packages
Builds and maintains security plans and authorization packages, including FedRAMP and OSCAL exports.
AI-assisted GRC
RegML AI agents assist with documentation, audits, risk assessments, evidence mapping, and control analysis.
RegScale pricing
RegScale uses quote-based annual subscriptions and offers a free Community Edition. Carahsoft lists ATO Automation Base SaaS at $133,900 annually, Policy & Compliance at $303,594.44, and Continuous Controls Monitoring Platinum at $309,000. AWS Marketplace supports contract purchasing.
| Plan | Price | What's included |
|---|---|---|
| Community Edition | Free | Core community deployment for compliance and GRC workflows |
| ATO Automation Base | From $133,900/yr | Base SaaS ATO automation license |
| Policy & Compliance | $303,594.44/yr | SaaS policy and compliance license subscription |
| Continuous Controls Monitoring Platinum | $309,000/yr | SaaS CCM Platinum tier license subscription |
| ATO Automation Landing Zone | $852,583/yr | SaaS landing-zone ATO automation license |
Free trial: No free trial is listed; a free Community Edition is available.
Pros & cons
Pros
- Continuous monitoring and automated evidence collection reduce reliance on spreadsheet- and document-driven audit preparation.
- OSCAL and compliance-as-code support fits engineering-led federal and highly regulated programs.
- Cross-framework mapping lets teams reuse common controls across multiple obligations.
- FedRAMP High authorization and air-gapped deployment support address demanding government environments.
Cons
- Public enterprise pricing is high, quote-based, and difficult to compare without a sales process.
- The G2 sample is very small at three reviews and averages 3.8/5.
- Reviews describe reporting, filtering, and customization as cumbersome in some workflows.
- Its breadth and implementation requirements may exceed the needs of a small company pursuing one basic certification.
Who is RegScale best for?
- RegScale is best for federal agencies and contractors building or maintaining FedRAMP and NIST authorization packages.
- It suits large enterprises that must map controls across several security and regulatory frameworks.
- Security engineering teams can use it to embed compliance checks into CI/CD and DevSecOps workflows.
- Organizations needing cloud, on-premises, or air-gapped deployment can match those requirements with its deployment options.
Frameworks and use cases
Integrations
Notable customers
Frequently asked questions
How much does RegScale cost?
+
RegScale does not publish ordinary list pricing. Carahsoft lists annual prices from $133,900 for ATO Automation Base SaaS, $303,594.44 for Policy & Compliance, and $309,000 for CCM Platinum; final enterprise pricing is contract-based.
How does RegScale work and how long does implementation take?
+
It connects security, cloud, scanner, ITIL, and DevOps data to machine-readable controls, then automates evidence, testing, workflows, and reporting. Implementation time depends on frameworks, integrations, deployment model, and authorization scope.
How does RegScale compare with Vanta?
+
Vanta is generally positioned around streamlined startup and mid-market certifications, while RegScale targets complex federal and enterprise programs with compliance-as-code, OSCAL, continuous controls monitoring, and on-premises or air-gapped deployment.
What integrations does RegScale support?
+
Named integrations include AWS, Azure, Google Cloud, ServiceNow, Jira, Salesforce, Tenable, Qualys, Wiz, Axonius, QRadar, and CSAM. The company says it has 75-plus integrations, APIs, webhooks, and more than 2,000 REST API endpoints.
Who is RegScale for?
+
Its primary buyers are federal agencies, defense contractors, financial-services and technology companies, and other organizations with complex multi-framework compliance. It is less suited to a small business seeking a simple, low-cost SOC 2 checklist.
Is RegScale secure and accurate for audit work?
+
RegScale has FedRAMP High authorization and supports cloud, on-premises, and air-gapped deployment. Buyers still need to validate mappings, configure integrations, and review AI-assisted outputs; G2 feedback is limited to three reviews.
Sources
Facts and pricing verified on October 19, 2026. Vendors change pricing often, so confirm with RegScale before buying. How we research